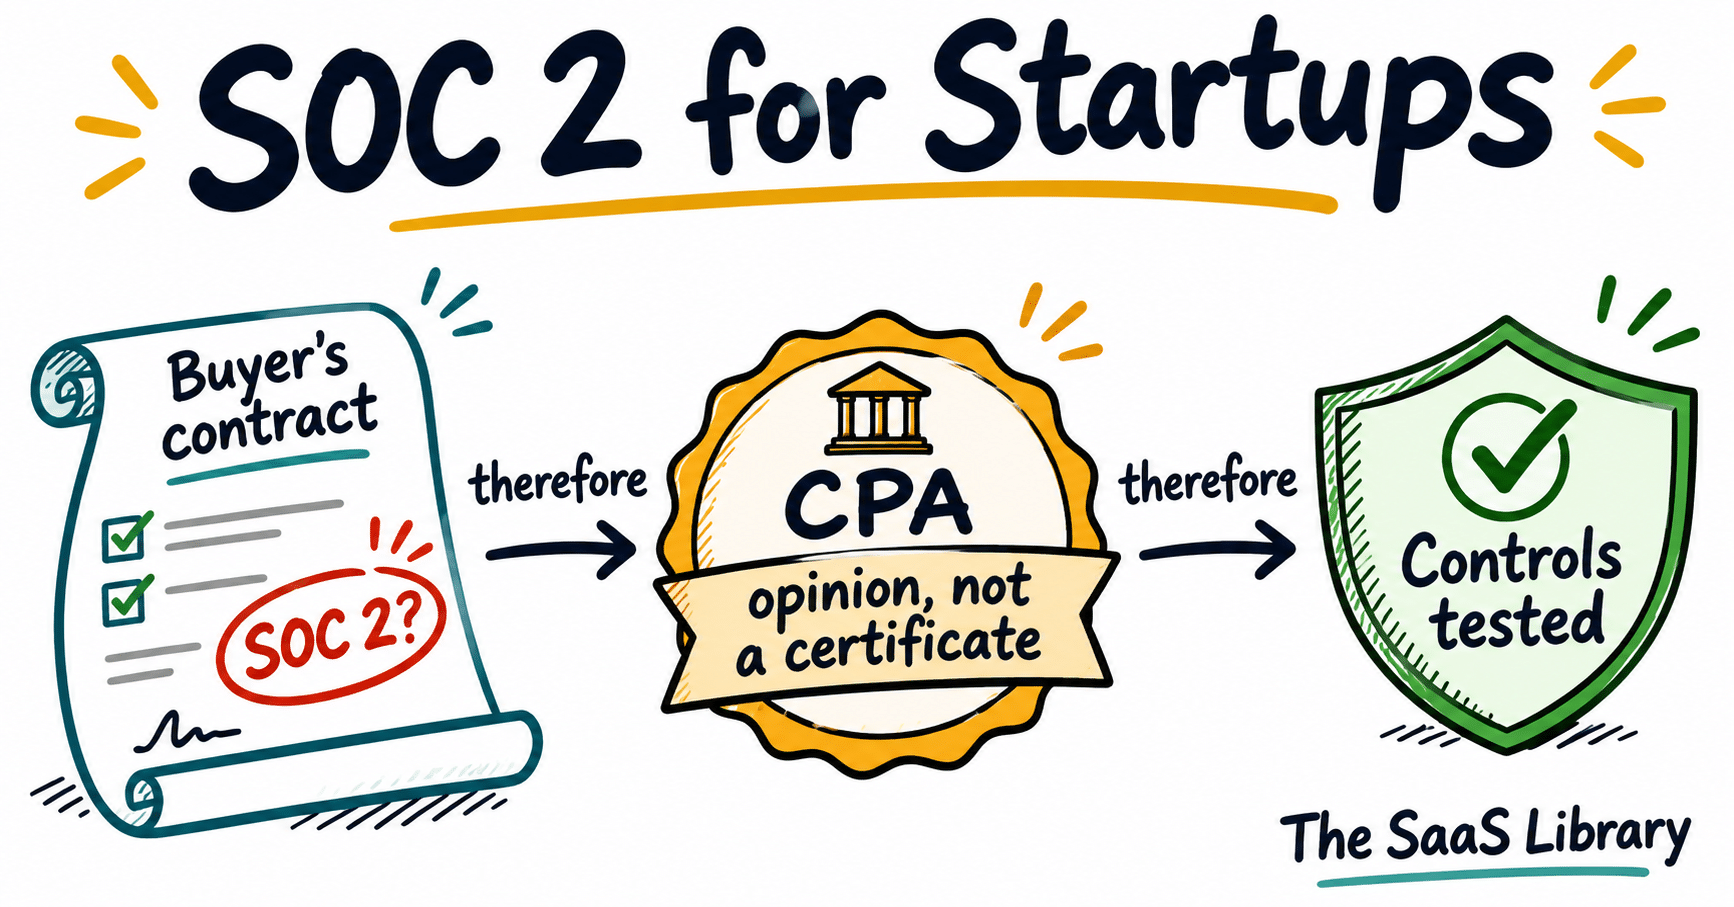
SOC 2 is not a certificate, and no law requires it, yet buyers keep asking for it. In ISC2’s 2025 survey, 77% of cybersecurity professionals said compliance with a standard such as SOC 2 or ISO 27001 was their top vendor requirement.
SOC 2 for startups means a CPA firm’s written opinion on how well your company’s controls meet the AICPA’s Trust Services Criteria. It is an attestation report, not a certificate, and no law requires it. Buyers ask for it because their contracts and security reviews do. This guide covers what SOC 2 proves, when a startup needs it, what it costs, and the risks to check before signing.
What is SOC 2, and what does it prove?
SOC 2 is an examination report in which a CPA expresses an opinion on a service organization’s controls. The controls are measured against the AICPA’s 2017 Trust Services Criteria, which define five categories: security, availability, processing integrity, confidentiality, and privacy. [TSP 100 ¶.09, ¶.11, ¶.20]
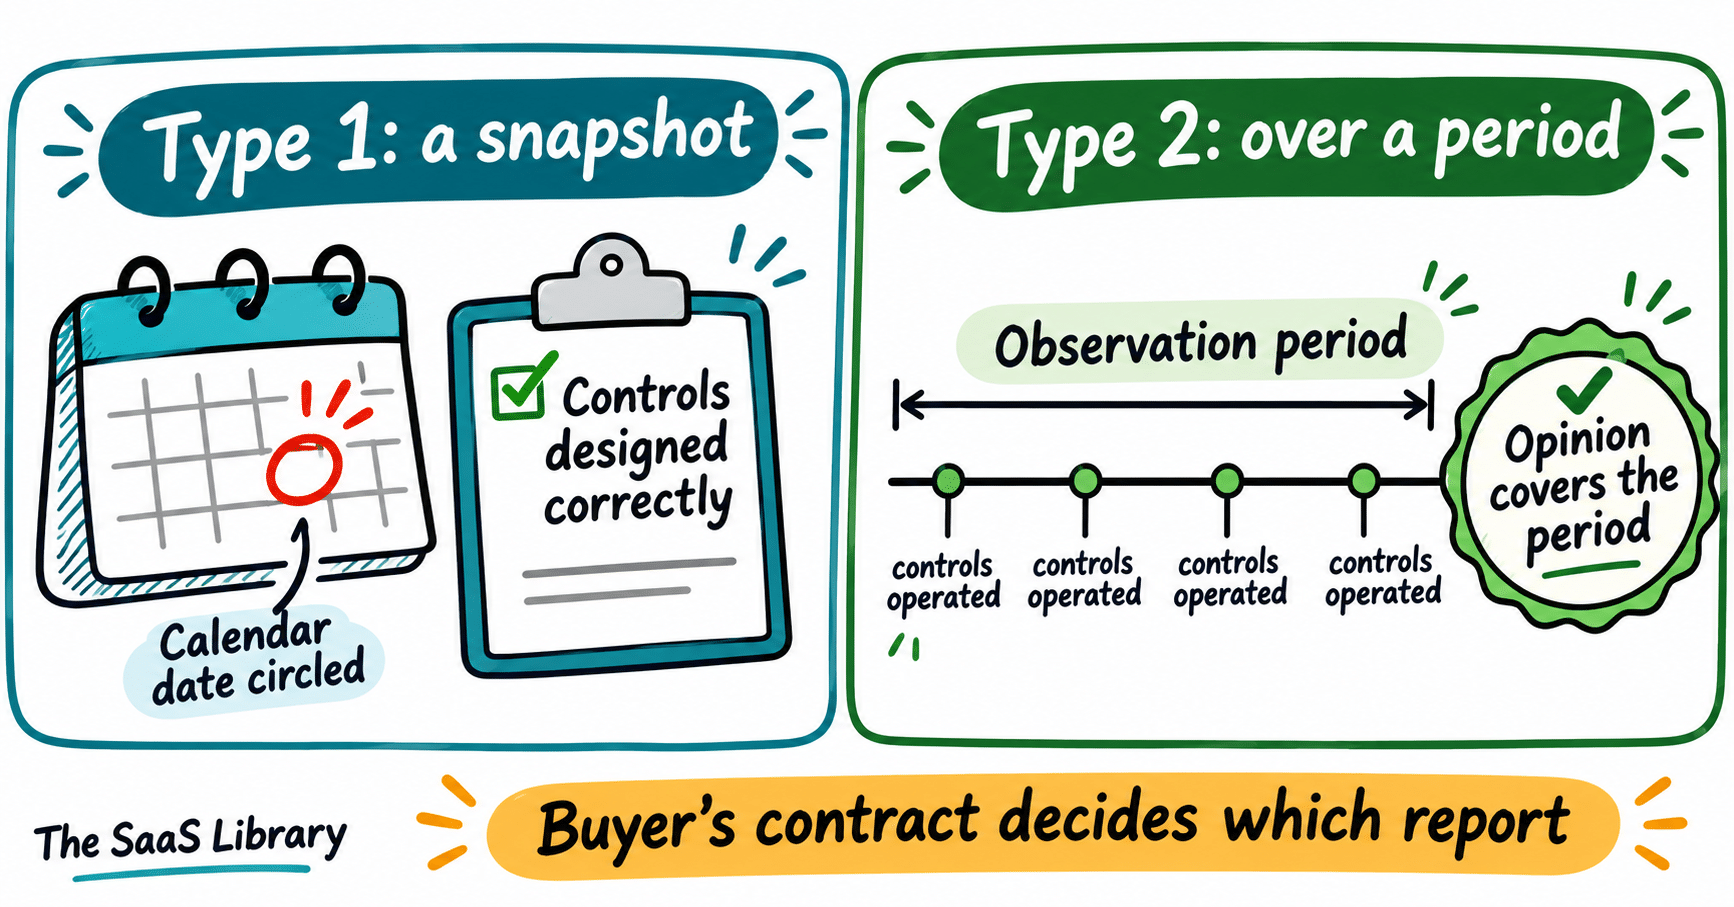
The AICPA defines the two report types by what each one tests. A Type 2 engagement covers “the suitability of design and operating effectiveness of controls… throughout a specified period.” A Type 1 engagement “addresses the same subject matter” but “does not contain an opinion on the operating effectiveness of controls nor a detailed description of tests of controls performed by the service auditor and the results of those tests.” [TSP 100 ¶.11]
| Dimension | Type 1 | Type 2 |
|---|---|---|
| What it tests | Design of controls at one point in time | Design and operation over a specified period |
| Opinion on operating effectiveness | No | Yes |
| Detailed test results | Not included | Included |
Source: AICPA TSP Section 100, ¶.11.
A Type 1 answers whether your controls are designed correctly on one day. A Type 2 answers whether they worked over a period, which is the question most buyers are asking.
Do you need SOC 2 yet?
You need SOC 2 when a customer or procurement process requires it, because SOC 2 is a voluntary attestation rather than a legal requirement. Whether you need it depends on what the contract asks for, including the report type, scope and coverage period. [A-LIGN; sample clause, LawInsider]
Buyers are where the demand comes from. In ISC2’s 2025 survey, “over three-quarters (77%) of participants cite compliance with standards (e.g., ISO 27001, NIST, SOC 2) as their top requirement.” [ISC2, 2025 Supply Chain Risk Survey] The same survey found that 71% of organizations require security audits, attestations or assessments from vendors.
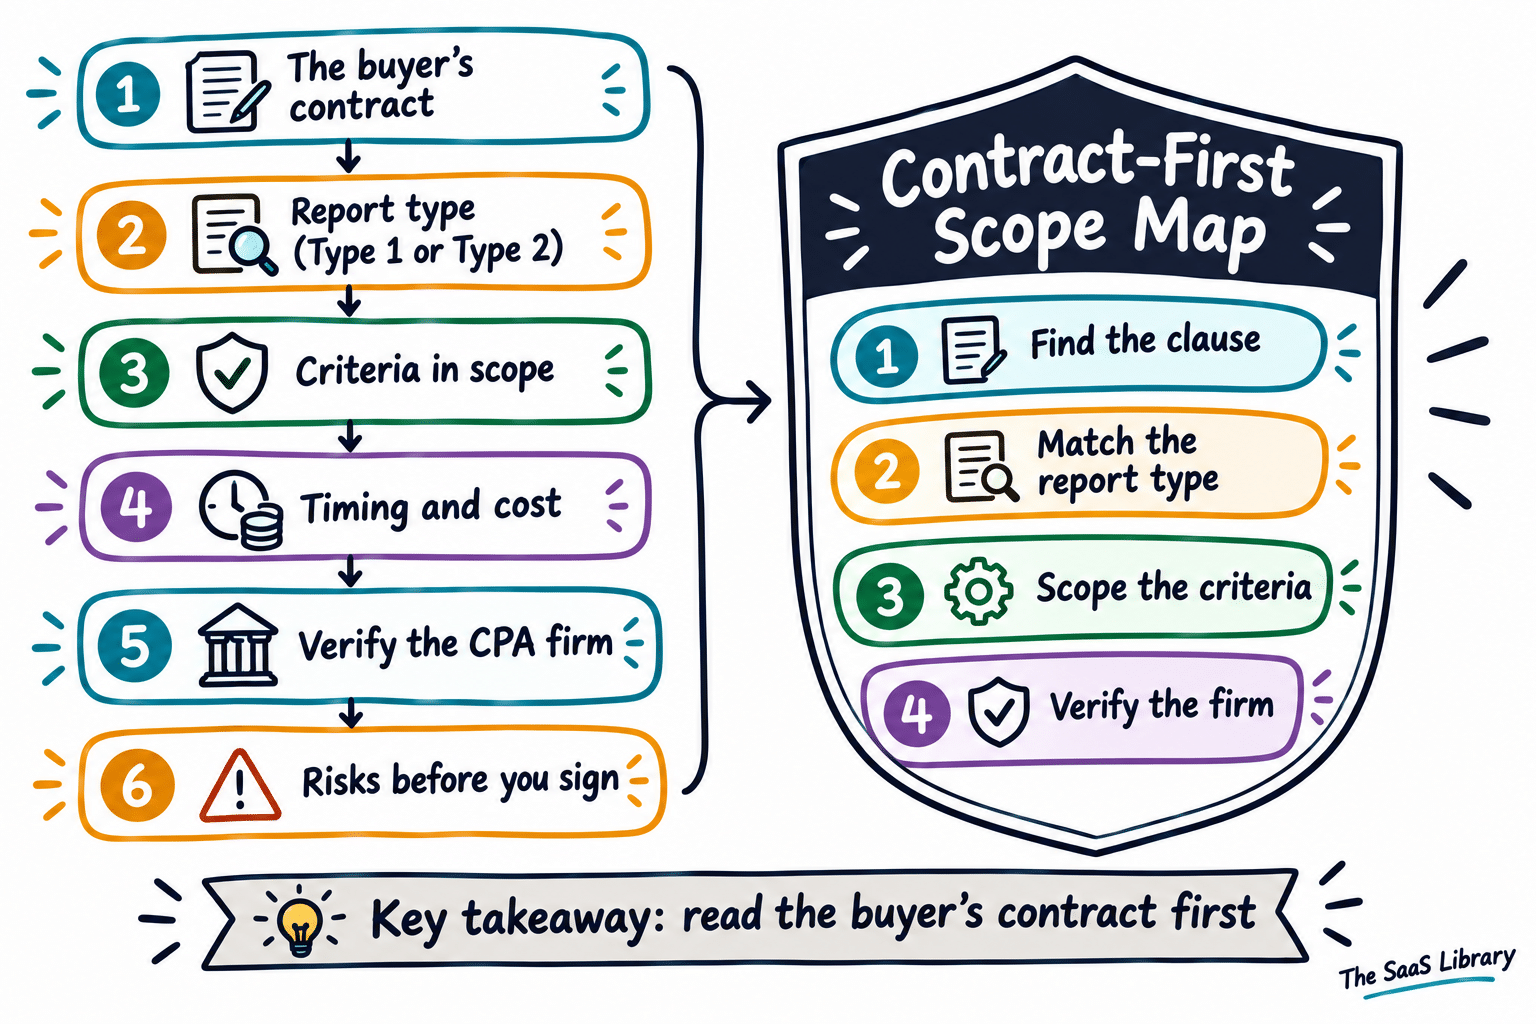
This guide uses a four-step method, the Contract-First Scope Map, to decide what SOC 2 your company needs. It starts with the buyer’s contract, because the contract sets the report type, scope and coverage period. The four steps are: find the clause, match the report type, scope the criteria, and verify the CPA firm.
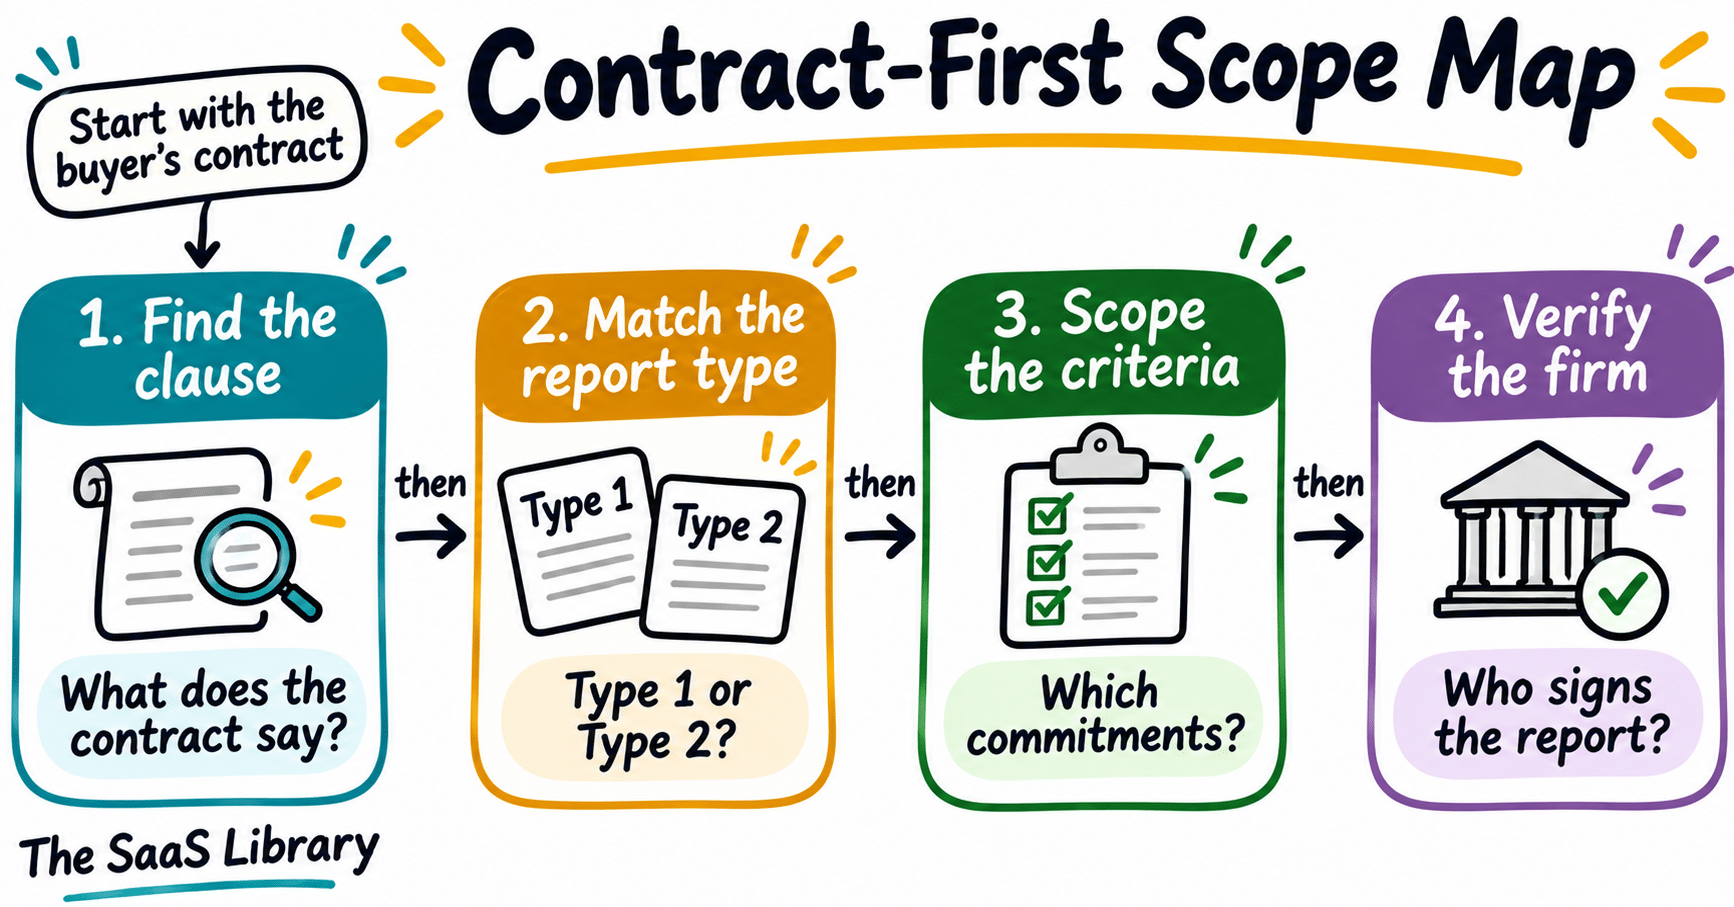
The buyer’s contract, not your company’s size or stage, sets the report type, scope and coverage period you need.
77% of cybersecurity professionals cite compliance with a standard such as SOC 2 or ISO 27001 as their top requirement. The figure covers any listed standard, not SOC 2 alone. [ISC2, 2025 Supply Chain Risk Survey]
Read more B2B SaaS analysis from The SaaS Library.
Browse B2B SaaS articles →Which SOC 2 report does your buyer need: Type 1 or Type 2?
A SOC 2 Type 1 report tests whether controls are designed correctly as of one date. A Type 2 report also tests whether they operated effectively over a specified period. Which one you need depends on what the buyer’s contract or questionnaire accepts. [TSP 100 ¶.11]
The AICPA’s definitions answer the technical question. The buyer’s contract answers the commercial one. Sample clause language published by LawInsider shows how a contract can name a specific report type. [sample clause, LawInsider; labelled as sample language]
The observation period, usually between three and twelve months, is market practice. The AICPA criteria do not set a length.
In one survey of SOC reports, Lazarus Alliance reported that 73% of the reports it reviewed were Type 2. This is one firm’s figure, not a market-wide measure. [Lazarus Alliance; attributed]
Which Trust Services Criteria should you scope?
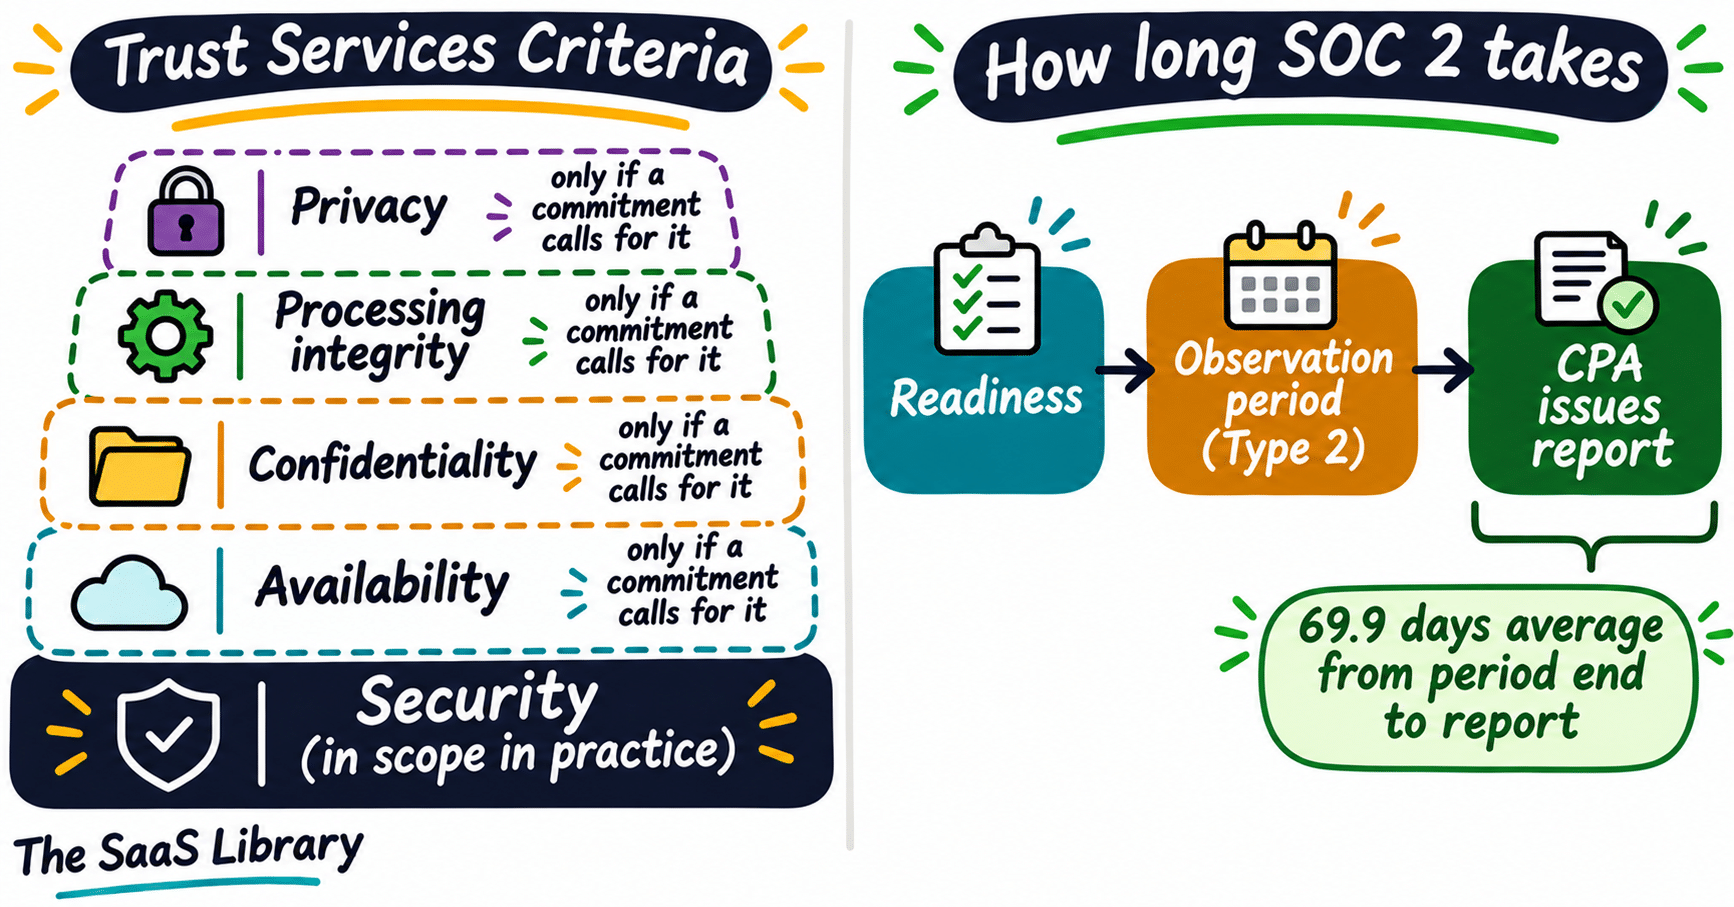
You should scope the Trust Services Criteria to the commitments you make to customers. Security is always in scope in practice, because the common criteria underlie every category. You should add Availability, Confidentiality, Processing Integrity or Privacy only when a commitment or customer requirement calls for it. [TSP 100 ¶.07, ¶.08, ¶.14]
The AICPA ties scope to what you have promised. Commitments “generally are included in written contracts, service level agreements, or public statements.” [TSP 100 ¶.14]
Across 73 SOC 2 reports reviewed by CBIZ in 2024, the share including each category was:
| Category | Share of reports |
|---|---|
| Security | 100% |
| Availability | 75.3% |
| Confidentiality | 64.4% |
| Processing integrity | 13.7% |
| Privacy | 6.8% |
Source: CBIZ 2024 SOC Benchmark. Security appears in every report because it is the base of the criteria, not because the AICPA requires it for every SOC 2.
How long does SOC 2 take for a startup?
SOC 2 takes as long as your readiness work, plus the observation period for a Type 2, plus the time the CPA firm needs to issue the report. In CBIZ’s 2024 benchmark, reports were issued an average of 69.9 days after the audit period ended. [CBIZ 2024 SOC Benchmark, Part Three]
| Stage | What drives its length | Figure |
|---|---|---|
| Readiness | Your controls, tooling, and evidence | Not measured by any primary source |
| Observation period (Type 2) | Contract and market practice | Usually 3 to 12 months (practice) |
| Report issuance | CPA firm’s review and report | Average 69.9 days after period end; 85% within 100 days |
The CBIZ figures combine SOC 1 and SOC 2 reports, across 193 reports, so they are not a startup sample. [CBIZ 2024]
Worked example (illustrative arithmetic, not a finding). A six-month observation period is about 182 days. Adding the 70-day average gives about 252 days, roughly eight months from start to report, before readiness work begins.
That covers what SOC 2 proves, which report your buyer needs, which criteria to scope, and how long it takes. The rest covers cost, what auditors check, how to verify the CPA firm, the risks to check before you sign, and the ISO 27001 and India questions.
How much does SOC 2 cost for a startup?
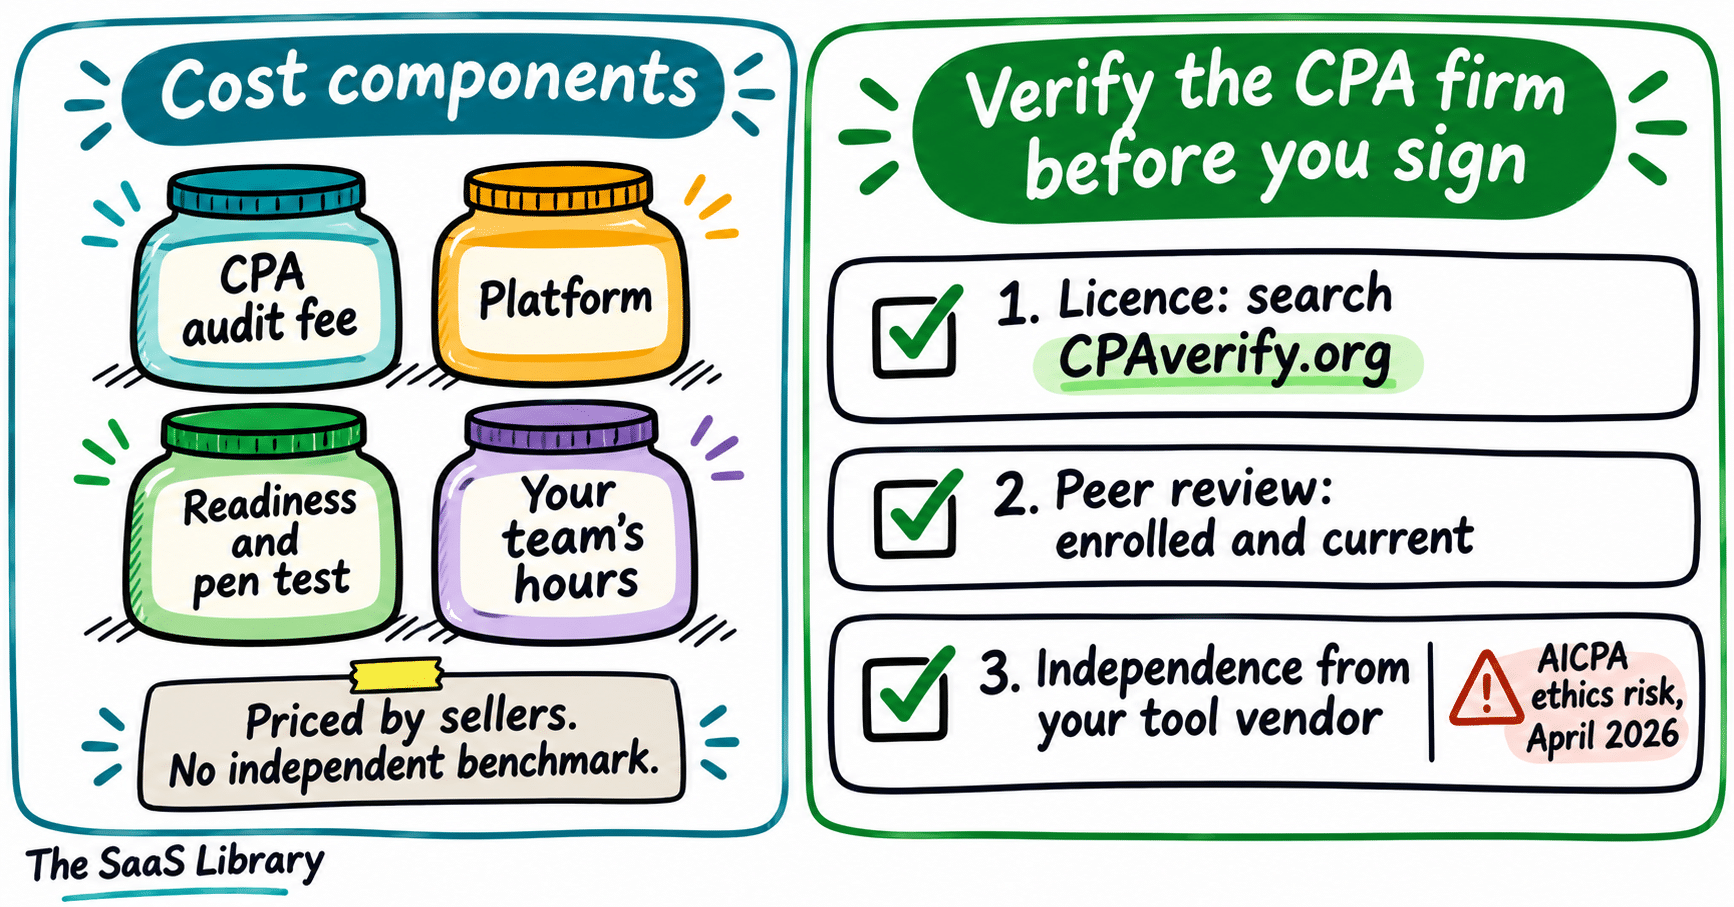
A SOC 2 for a startup costs more than the CPA audit fee alone, because readiness, tooling, testing and internal time are separate costs. Published audit fees range widely, from about $3,000 for a Security-only Type I at one firm to $200,000 for a Big Four Type 2 in one directory’s estimate. [Auditsuisse; soc2auditors.org]
No primary source publishes SOC 2 prices. Every figure is set by a seller, a directory, or a consultant, and none is an independent benchmark.
| Cost component | What it covers | Published example | Source type |
|---|---|---|---|
| CPA audit fee | Examination and signed report | Type 2, specialist firm: $15,500–$50,000 | Directory estimate |
| CPA audit fee, fixed | One firm’s published schedule | Type 2, Security only, 1–50 employees: $5,000 | Firm’s own price |
| Platform | Evidence collection and controls software | $7,800/year, bundled | Vendor |
| Readiness, pen test, internal time | Closing gaps, third-party testing, staff hours | Not priced: no primary source | None |
Sources: soc2auditors.org; Auditsuisse; Polara Labs.
Why quotes differ. Scope, firm tier, readiness, and whether a quote covers the audit fee or a bundle. Directory bands show the tier effect: a specialist and a full-service firm can differ by a factor of two or more for the same Type 2.
Reader implication: Ask every quote to list the audit fee separately from the platform, readiness, pen test, and your team’s hours. Quotes that can’t be split can’t be compared.
What do auditors actually check?
Auditors check whether the controls you described meet the Trust Services Criteria in scope, and whether they operated throughout the observation period. The criteria name the areas, such as logical access, change management and vendor risk. [TSP 100 ¶.20 and criteria table]
| Area | Criterion | What the AICPA says a control should do |
|---|---|---|
| Access reviews | CC6.2 | “The appropriateness of access credentials is reviewed on a periodic basis for unnecessary and inappropriate individuals with credentials.” |
| Offboarding | CC6.3 | “Processes are in place to remove access to protected information assets when an individual no longer requires access.” |
| Change management | CC8.1 | “A process is in place to authorize system changes prior to development.” |
Source: AICPA TSP Section 100 (March 2020 copy).
A Type 2 auditor tests whether these controls worked during the period, not only whether they exist. An access review that happened once, at the start, does not meet a criterion that requires periodic review. [TSP 100 ¶.11]
How do you verify the CPA firm behind your report?
You verify the CPA firm by checking three things: that it holds a valid CPA firm licence, that it is enrolled in the AICPA Peer Review Program, and that it has no business arrangement with your tool vendor that compromises independence. [NASBA; NYS Office of the Professions; AICPA]
Check 1: the licence. Search the firm and the signing CPA on CPAverify.org. The database is “populated by official, publicly available, licensing data sent directly from the Boards of Accountancy.” [NASBA, March 2026]
Check 2: peer review. New York requires firms performing attest services to enroll in the peer review program and complete the review within 18 months of starting that work. [NYS Office of the Professions]
Check 3: independence from your tool vendor. The AICPA states that business arrangements with SOC tool providers “can raise significant threats to compliance with the Code of Professional Conduct.” [AICPA, Ethics Staff Insights, April 2026] Auditors must evaluate any arrangement that could shift “access to evidence away from the auditor and toward the tool provider.” [Journal of Accountancy, April 2026]
What risks should you check before you sign?
Before you sign, you should check four risks: that the report type matches the buyer’s contract, that the coverage period and any bridge letter are agreed, that the auditor’s independence from your tool vendor is documented, and that your controls operate in practice, not only on paper. [TSP 100 ¶.11; CBIZ 2024; AICPA]
| Risk | What can go wrong | Evidence | Status |
|---|---|---|---|
| Report type | Type 1 accepted where the buyer needs Type 2 | TSP 100 ¶.11 | Verified |
| Coverage gap | Report period ends before the buyer’s review | Bridge letter practice | Practice |
| Auditor independence | Tool vendor’s arrangement shifts control or evidence access | AICPA Ethics; Journal of Accountancy, April 2026 | Verified |
| Exceptions | Control failures reported in the opinion | 54.9% had at least one exception (CBIZ 2024) | Verified |
| Qualified opinions | Opinion modified because of failures | 10.9% qualified (CBIZ 2024) | Verified |
| Contract limits | Buyer receives a summary, not the full report | Twilio 2024 terms | Verified |
| AI and agents | Tools outside the system description may create risk the report does not cover. See the AI agent governance gap and AI compliance for enterprise SaaS. | AICPA assurance work in development | Scope inference |
| Unsanctioned tools | Tools your team uses without approval fall outside the report. See shadow AI tools in your SaaS stack. | Scope inference | Practice |
| Agent access to systems | Agents that reach in-scope systems create access and change-control risk. See MCP security vulnerabilities. | Scope inference | Practice |
CBIZ found that “there is no requirement to document why reports aren’t qualified,” so an unqualified opinion does not itself prove that no exceptions occurred. [CBIZ 2024 SOC Benchmark]
Illustrative example. A buyer asks for a Type 2 covering the last twelve months, and your report covers six. The gap is a contract problem, not an audit problem, and it is caught only by reading the coverage period against the contract.
How does SOC 2 compare with ISO 27001?
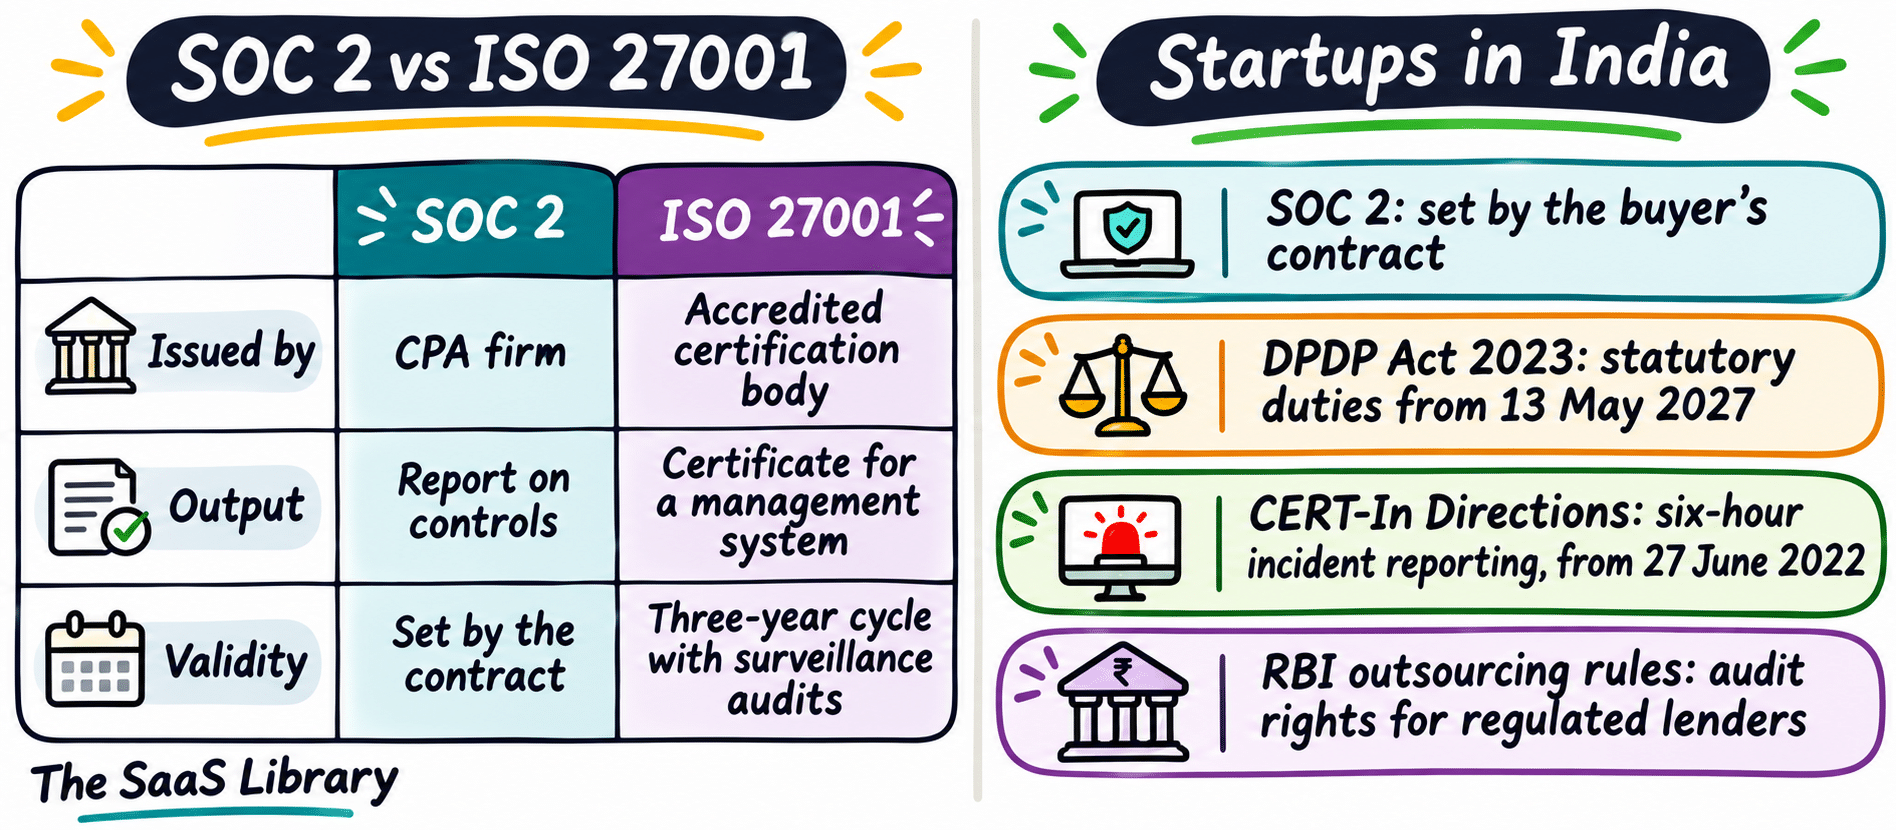
SOC 2 is a CPA attestation report on controls against the AICPA’s Trust Services Criteria, while ISO 27001 is a certificate that an accredited certification body issues after auditing an information security management system against the ISO standard. Choose between them based on what your buyers’ contracts name. [TSP 100 ¶.20; Linford & Co]
| Dimension | SOC 2 | ISO 27001 |
|---|---|---|
| Governing body | AICPA | ISO and IEC |
| What is delivered | CPA opinion report with test results (Type 2) | Certificate issued by a certification body |
| Who issues it | Licensed CPA firm | Accredited certification body |
| What is measured | Controls against the criteria you scoped | The management system against the standard |
| Validity | No AICPA term; annual renewal is practice | Three years, with surveillance audits |
ISO rows rest on certification-body sources. The ISO home listing confirms ISO/IEC 27001:2022, Edition 3, titled “Information security management systems — Requirements.”
The accreditation question. Most practitioners say a certificate from an accredited body is the one buyers recognize. One reference says accreditation “is not compulsory.” Ask any certification body for its accreditation body and scope before you rely on the certificate.
Illustrative example. A US enterprise buyer asks for a SOC 2 Type 2 report. A European buyer asks for an ISO 27001 certificate. A SaaS company may need both, and one does not substitute for the other.
Do startups in India need SOC 2?
No Indian law requires SOC 2 for a startup. Indian SaaS companies usually need it because US and European buyers ask for it in contracts, while the DPDP Act 2023 is a separate statutory obligation for processing personal data. If you serve regulated Indian lenders, RBI outsourcing rules add their own audit and incident-reporting duties. [MeitY, DPDP Rules 2025; RBI Master Direction]
| Obligation | Source of authority | Who it applies to | Timing |
|---|---|---|---|
| SOC 2 report | Buyer contract | Companies whose buyers ask for it | Set by the contract |
| DPDP Act 2023 and Rules 2025 | Statute and rules | Anyone processing digital personal data in India | Rules 1, 2 and 17 to 21 on publication; Rule 4 on 13 November 2026; Rules 3, 5 to 16, 22 and 23 on 13 May 2027 |
| CERT-In Directions | Under s.70B(6) of the IT Act | Service providers and bodies corporate | Effective 27 June 2022; six-hour reporting; 180-day logs in India |
| RBI IT outsourcing Direction | RBI/2023-24/102 | Regulated entities, and vendors through contract | Contract and audit requirements |
The Rules were amended by corrigendum G.S.R. 892(E), which changed the commencement wording to “in the Official Gazette.” The dates above are unchanged. [MeitY, G.S.R. 846(E) and G.S.R. 892(E)]
RBI, precisely. The RBI Direction requires audit rights over outsourced IT services, including over sub-contractors, and allows several entities sharing a provider to conduct one pooled audit. The excerpt we reviewed does not name SOC 2, so this article does not say RBI requires it. [RBI, 10 April 2023]
Illustrative example. A Bengaluru SaaS company sells to a US retailer, and its contract requires a SOC 2 Type 2. It also stores personal data of Indian users, so the DPDP duties apply on their own terms. If it sells to an Indian NBFC, that lender’s contract will push RBI audit clauses down to the vendor. One SOC 2 report covers none of these three.
Frequently Asked Questions
What is SOC 2 compliance?
SOC 2 is a CPA firm’s opinion report on controls measured against the AICPA’s Trust Services Criteria. It is an attestation, not a certificate.
Is SOC 2 a certification?
No. SOC 2 is an attestation report issued by a CPA firm, not a certificate from a certifying body.
Do I need SOC 2 yet?
You need SOC 2 when a customer or procurement process requires it, because it is a voluntary attestation rather than a legal requirement.
Is SOC 2 mandatory in India?
No Indian law requires it. US and European buyers often require it in contracts, while the DPDP Act 2023 is a separate statutory obligation.
Is SOC 2 better than ISO 27001?
Neither is better in general. Choose based on what your buyers’ contracts name.
Type 1 or Type 2: which do I need?
Whichever report your buyer’s contract or questionnaire accepts. A Type 1 tests design as of one date. A Type 2 also tests operation over a specified period.
Is a Type 1 enough?
Only if the buyer accepts it. A Type 1 contains no opinion on operating effectiveness.
How long does SOC 2 take?
Readiness, plus the observation period for a Type 2, plus the CPA firm’s time to issue the report. CBIZ’s 2024 benchmark found reports were issued an average of 69.9 days after the audit period ended.
How much does SOC 2 cost?
The audit fee is only one part. Published fees vary widely by firm tier and scope, and no primary source sets a benchmark.
What do auditors check?
The criteria in scope, such as logical access, change management and vendor risk, tested over the period.
Conclusion
SOC 2 for startups is a CPA firm’s opinion on your controls, measured against the AICPA’s Trust Services Criteria. It is an attestation, not a certificate, and no law requires it. You need it when a buyer’s contract or security review asks for it, and that contract also sets the report type, scope and coverage period.
Plan the timeline backward from the deal date, and treat each cost as a separate line item. Before you start, read the security section of your largest open deal and write down what it asks for.
- AICPA, TSP Section 100: 2017 Trust Services Criteria (March 2020 copy)
- AICPA, 2017 Trust Services Criteria with revised points of focus (2022)
- AICPA, System and Organization Controls landing page
- AICPA, Ethics Staff Insights: Business arrangements with SOC tool providers (April 2026)
- Journal of Accountancy, SOC engagements: Ethics risks with tool providers (April 2026)
- Linford & Co, What is SOC 2?
- Linford & Co, ISO 27001 compliance assessment
- A-LIGN, What is SOC 2? A complete guide
- ISC2, 2025 Supply Chain Risk Survey
- LawInsider, SOC 2 Type 2 report sample clause
- CBIZ, 2024 SOC Benchmark (full report, PDF)
- CBIZ, The Evolution of SOC Reporting, Part Three (2024 SOC Benchmark)
- CBIZ, The Evolution of SOC Reporting, Part Two (2024 SOC Benchmark)
- soc2auditors.org, SOC 2 audit cost
- Auditsuisse, SOC 2 pricing
- Polara Labs, SOC 2 cost
- NASBA, All about CPAverify (March 2026)
- New York State Office of the Professions, Mandatory Peer Review
- Alabama Society of CPAs, Partners in Peer Review
- MeitY, Digital Personal Data Protection Rules, 2025 (G.S.R. 846(E))
- MeitY, Corrigenda to DPDP Rules, 2025 (G.S.R. 892(E), 10 December 2025)
- PIB, DPDP Rules notified (14 November 2025)
- RBI, Master Direction on Outsourcing of IT Services, RBI/2023-24/102 (10 April 2023; copy hosted by FIDC)
- CERT-In, Directions under Section 70B(6), No. 20(3)/2022-CERT-In (28 April 2022)
- ISO, ISO/IEC 27001:2022 listing
- Wikipedia, ISO/IEC 27001 (accreditation dispute)
- Cyberhaven, What is ISO 27001?
- Twilio, Updates to Legal Terms and Conditions (12 November 2024)
- Figma, Software Services Agreement, Exhibit B section 20.1
- Figma, Trust Center